Introducing the Gamz REST API

Connecting Gamz to your website, reporting tools or other business systems just got simpler. Our new REST API is now available, giving developers a more straightforward way to work with Gamz data using standard HTTPS requests and JSON responses.
Built for the tools you already use
Some customers working on macOS, Linux and other non-Windows platforms found our previous SOAP integration difficult to consume. Getting the client tooling and security configuration working could take more effort than the integration itself.
The new REST API makes that connection easier. Your developer can use familiar HTTP clients and the backend language that suits your organisation, whether that is JavaScript, Python, PHP, Java or .NET. There are no SOAP envelopes or generated SOAP service proxies to configure for the new endpoints.
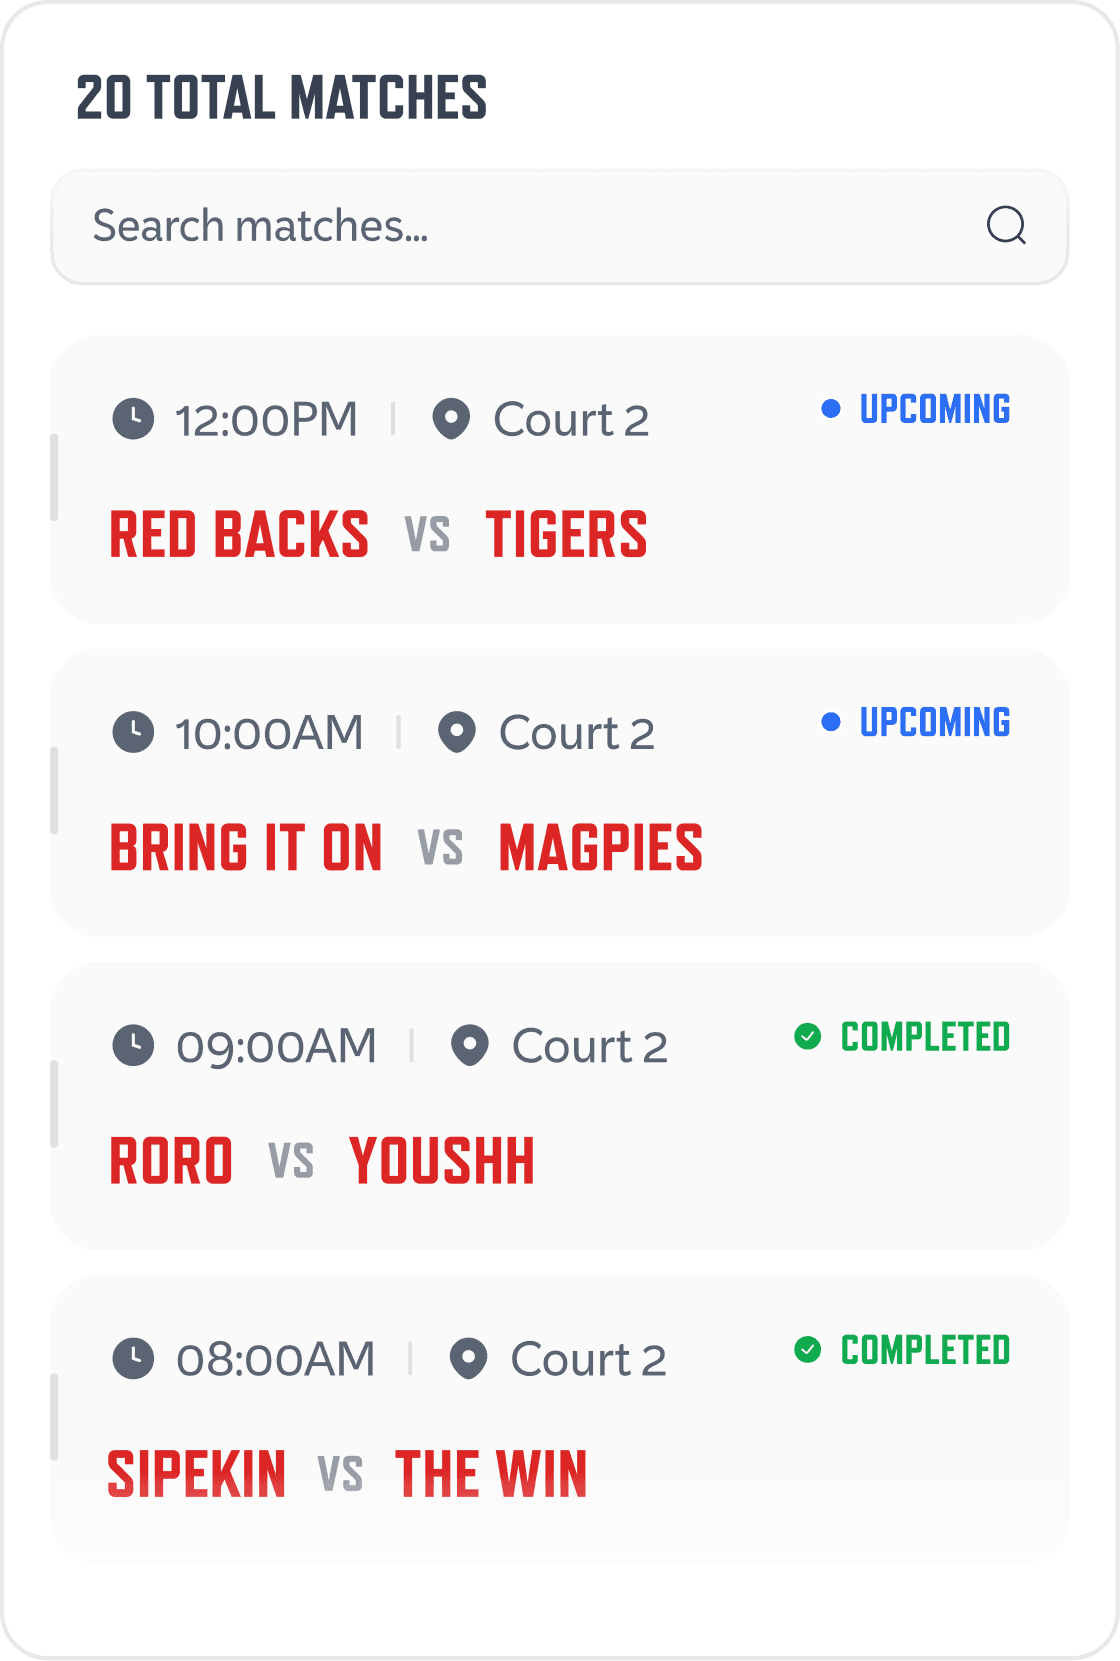
That means more time building useful connections, from a custom game-day dashboard to fixtures on your website.
The same core capabilities, now through REST
We have reproduced the core operations from the SOAP API as REST endpoints, so the jobs your integration performs can move to the new interface. These include:
Reading competition matches and bookings from the calendar.
Retrieving competition fixtures and ladders.
Recording payments collected outside Gamz against a player within a team.
The endpoint catalogue also covers public venue, competition, team, player and match information, plus authenticated operations for scoreboards and check-in. Your developer can review the available requests and response examples in the Gamz API documentation.
Straightforward bearer-token authentication
Private API requests use a bearer token. Start with API access for your venue, its ApplicationId and a dedicated API user account with active access to that venue.
Request a token by sending
username,passwordandapplicationIdas JSON toPOST https://api.gamzapp.com/rest/auth/token.Use the returned
access_tokenon private requests in the HTTP headerAuthorization: Bearer <access_token>.Reuse the token for its stated
expires_inlifetime, then request a new token when it expires.
Your integration uses the token for subsequent calls, so it does not need to send your username and password with every business request. Keep the credentials and tokens in your backend, protected like any other password.
The documented public read endpoints can be called without a bearer token. The guide clearly identifies which requests are public and which require sign-in.
Your starting point
The new API application root is https://api.gamzapp.com/rest/. The developer documentation includes setup guidance, authentication details, endpoint parameters, example requests and JSON responses.
For existing integrations, this is a migration rather than a change of hostname alone. Your developer will need to update the routes, replace SOAP requests with the documented HTTP and JSON requests, and implement token authentication for private calls.
Start building, or plan your migration
All new integrations should use the REST API. Existing customers should plan their move before 1 May 2027, when the legacy API services are being retired.
Share the API documentation with your developer or integration provider. If you need help confirming API access or finding the right endpoints, get in touch with the Gamz team.
We’re looking forward to seeing what you connect with Gamz.